Reduce Costs, Maximise Efficiency, Optimise Availability.
CNI Is Expanding. So Are the Responsibilities.
What Challenges Are Facing UK Critical Infrastructure?
An Expanded Definition of CNI
Navigating cyber regulation and compliance
Maximising operational resilience and recovery.
Modernising legacy networks and OT systems.
Transforming and futureproofing critical infrastructure.
Supporting the ongoing convergence of IT and OT.
Maintaining full asset visibility.
AI readiness and data-driven insights.
Securing the new breed of interconnected supply chain.
The Trusted Technology Partner for the UK's CNI Sector.
Consisting of Exponential-e, Vysiion, and Xpertex, the Exponential-e Group has spent more than 30 years delivering innovative IT/OT solutions for CNI. We combine deep sector-specific experience, leading-edge technologies, and a keen understanding of the evolving compliance landscape, providing us with a unique perspective on digital transformation for CNI. This allows us to deliver intelligently integrated, cyber-secured solutions in the most complex environments - with our own enterprise-class network underpinning everything. To this end, more than 250 of our 800+ employees are cleared to operate in the most highly secure, highly regulated environments across the country.
Proven Across Complex UK Infrastructure.

An Evolving CNI Technology Toolbox.
Secure Connectivity
Cyber Security
Sovereign Cloud Infrastructure
IT & OT Integration
Disaster Recovery & Business Continuity
Data & AI
, with the highest levels of security and sovereignty overlaying everything.
Managed IT Services
Unified Communications & Contact Centre
Know What Applies. Understand What to Do Next.
Answer three questions to identify the cyber regulations, frameworks and standards your organisation should consider, why they matter, and the security capabilities that can help you respond.
Find Your Framework Map.
Three quick questions turn a complex compliance landscape into a practical starting point.
Which Sector Do You Operate In?
Choose the closest match. You can change this at any point.
Where Do You Operate?
Geography can materially change which cyber regulations apply.
What Does Your Organisation Operate?
This distinguishes information-security requirements from industrial and operational cyber-security requirements.
Your Framework Starting Point
Need The Detail Behind These Frameworks?
Use the full Framework Selector for detailed requirements, framework explanations, Exponential-e solution mapping and deeper regulatory guidance.
Sector-Specific Journeys, One Connected CNI Proposition.
Utilities
Finance
Healthcare
Government
Manufacturing & Food
Emergency Services
Defence
Water Companies
Our Commitment to Delivering Excellence.
Independent Standards. Embedded Into Everything We Deliver.
Our independently audited accreditations provide assurance across environmental management, energy efficiency, quality, security, service management, resilience and Cloud security.
ISO 14001
Environmental Management
ISO 14001
Environmental Management

Independent assurance supporting Exponential-e’s standards-driven approach to service delivery.
ISO 9001
Quality Management
ISO 9001
Quality Management

Independent assurance supporting Exponential-e’s standards-driven approach to service delivery.
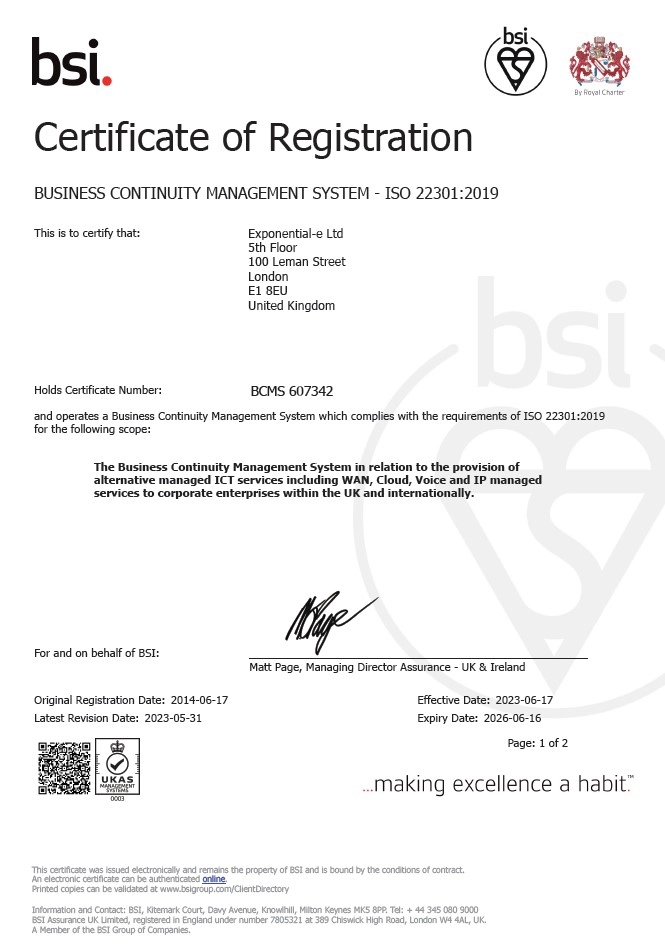
ISO 22301
Business Continuity Management
ISO 22301
Business Continuity Management

Independent assurance supporting Exponential-e’s standards-driven approach to service delivery.
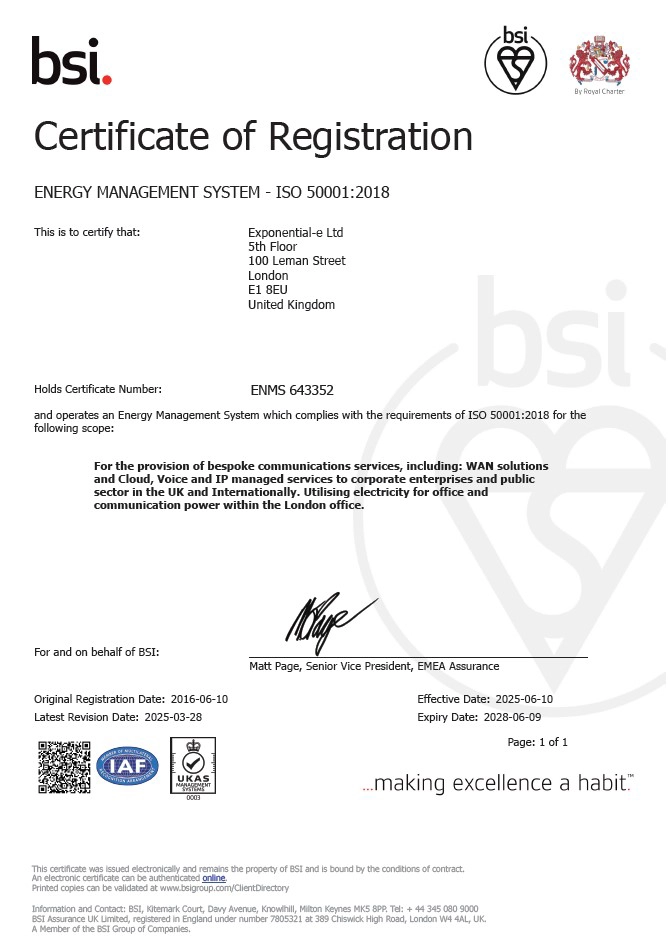
ISO 50001
Energy Management
ISO 50001
Energy Management

Independent assurance supporting Exponential-e’s standards-driven approach to service delivery.
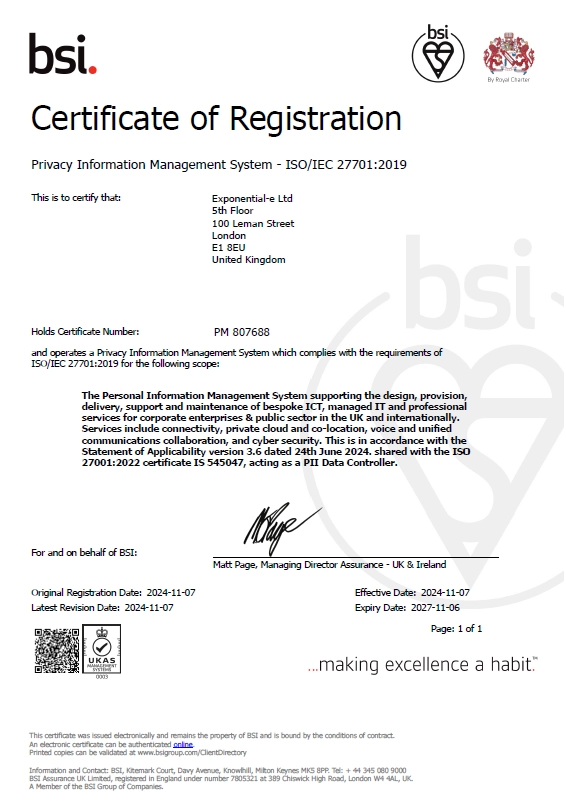
ISO/IEC 27701
Privacy Information Management System
ISO/IEC 27701
Privacy Information Management System

Independent assurance supporting Exponential-e’s standards-driven approach to service delivery.
ISO/IEC 27001
Information Security Management
ISO/IEC 27001
Information Security Management

Independent assurance supporting Exponential-e’s standards-driven approach to service delivery.
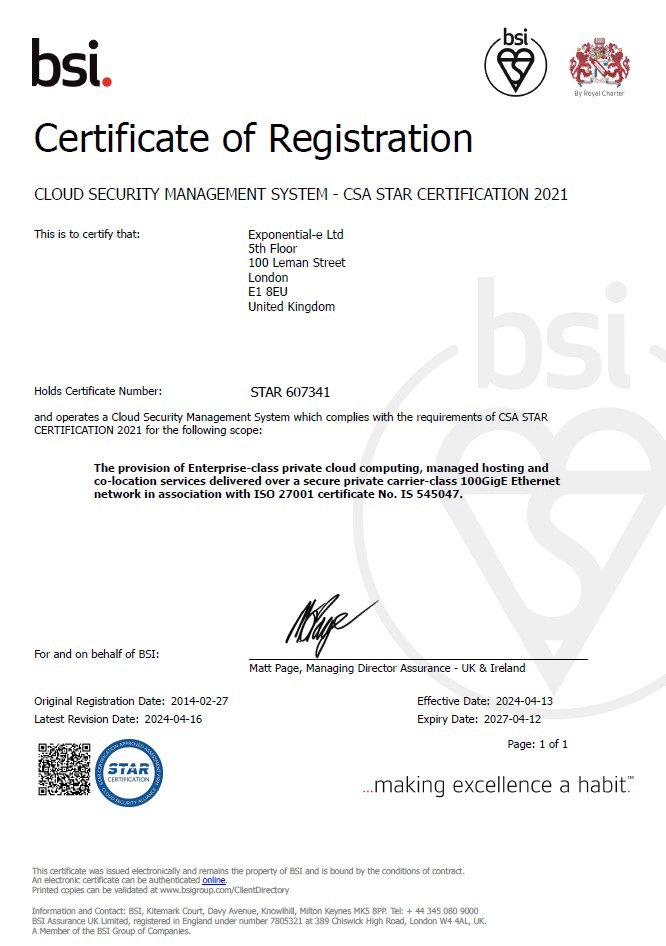
CSA STAR
Cloud Security
CSA STAR
Cloud Security

Independent assurance supporting Exponential-e’s standards-driven approach to service delivery.
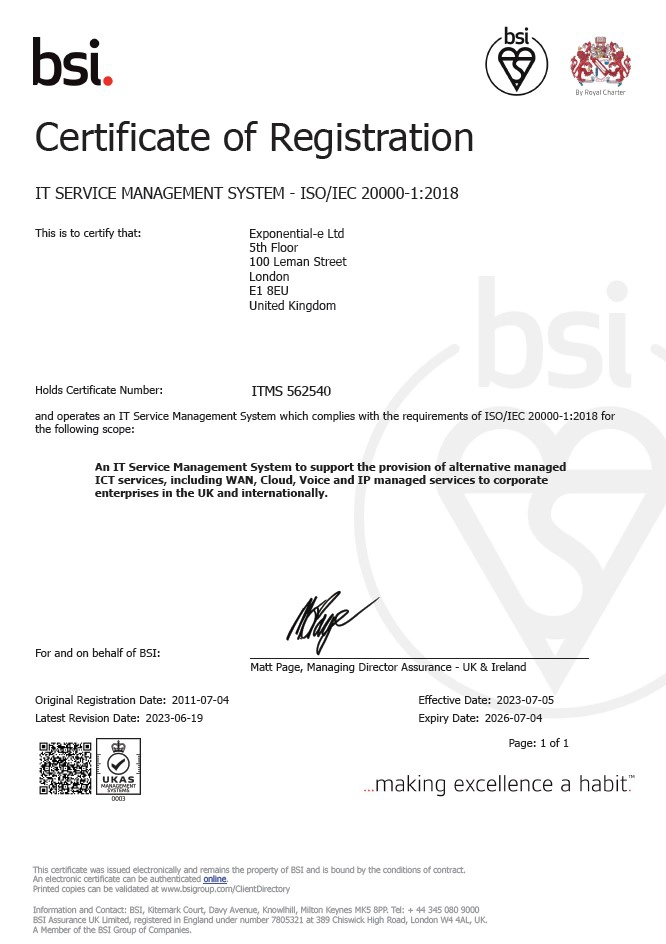
ISO/IEC 20000-1
Service Management
ISO/IEC 20000-1
Service Management

Independent assurance supporting Exponential-e’s standards-driven approach to service delivery.
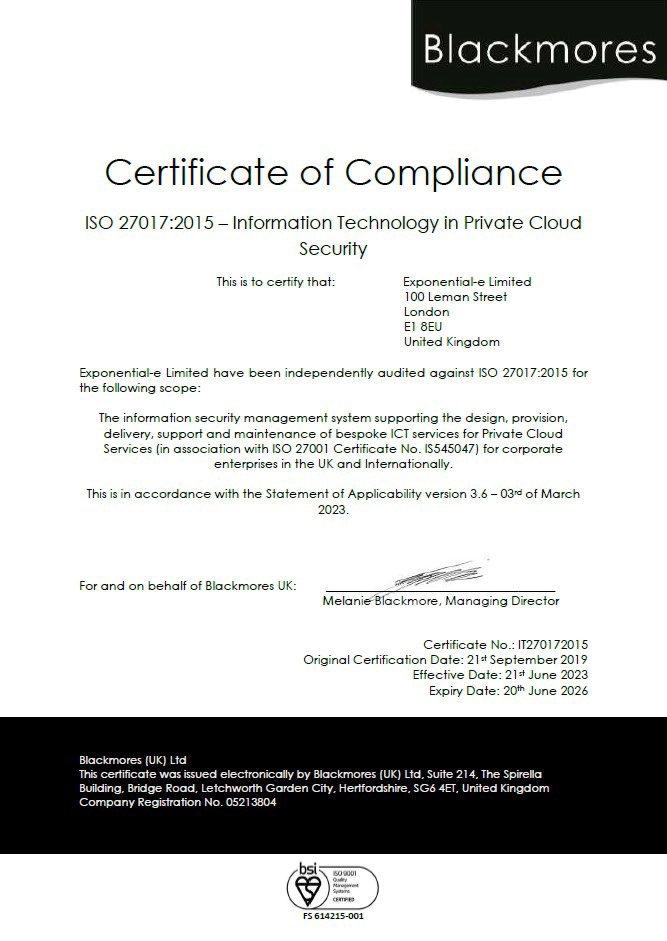
ISO 27017
Security Controls for Cloud Services
ISO 27017
Security Controls for Cloud Services

Independent assurance supporting Exponential-e’s standards-driven approach to service delivery.

How Do We Support Critical Infrastructure Organisations?
Explore real-life examples of how the Exponential-e Group’s ongoing support has helped CNI organisations achieve their digital goals, futureproof their foundational systems, and overcome the most complex operational and regulatory challenges.

Keeping Emergency Services Connected.
Resilient, always-on infrastructure supporting critical communications and ambulance services nationwide.

Protecting a Critical Energy Connection.
Integrated physical security, resilient infrastructure and real-time monitoring across a vital UK–France power interconnector.

Connecting Critical Infrastructure Offshore.
Secure, resilient communications connecting onshore operations, offshore infrastructure and critical control systems.
Intelligence for an Evolving Critical Infrastructure Landscape.
Explore the latest thinking from our CNI experts on cyber regulation, operational resilience, IT/OT convergence, AI, data sovereignty and the technologies transforming the UK’s critical services.

Secure, resilient, and always on.
Navigating compliance for the UK's Utilities sector For the UK's Utilities sector, compliance is not simply an annual box-ticking exercise. It's a foundational element of secure, seamless operations that ensure these critical services are readily ava...
Read More →
From Trusted Platforms to Exceptional Outcomes - Rethinking Data and AI at Scale
Mathematician Clive Humby said in 2006 that "Data is the new oil". Twenty years on, he has been proven right in ways he could never have anticipated. The increasing integration of physical and digital systems, followed by the rapid rise of Artificial...
Read More →
'Secure by design’ must become the new norm for mission-critical infrastructure
It is no secret that cyber security is a priority for all sectors, as threats evolve in terms of frequency, scale, and sophistication. However, for Operators of Essential Services (OESs), this is just part of a larger, more complex picture. With the ...
Read More →Critical Infrastructure. Clearly Explained.
Straightforward answers to key questions around CNI security, resilience, regulation, IT/OT convergence, data sovereignty and AI.
Critical National Infrastructure (CNI) refers to systems that power key national services, security, the economy, and public safety. This encompasses both physical and digital assets, including Operational Technology (OT) and connected devices, IT systems, Cloud platforms, and the ever-increasing streams of data they generate.
The UK Government’s definition of CNI has recently expanded, and now encompasses a range of sectors, including utilities, manufacturing, emergency services, defence and national security, data centres, healthcare, finance, and multiple Government organisations - all of whom have specific compliance obligations around security and resilience that must be considered.
CNI faces a diverse and evolving range of cyber threats, including (but not limited to) compromised identities, hidden vulnerabilities in legacy systems and converged IT/OT, limited asset visibility, and compromised supply chains and third parties. All of these represent potential attack vectors that must be considered as part of a robust CNI cyber strategy, taking into account the organisation’s specific operational environments and regulatory obligations.
The Cyber Assessment Framework (CAF) was launched by the National Cyber Security Centre (NCSC) to provide organisations with a structured approach to identifying and mitigating cyber risk. It offers an end-to-end approach to identifying, securing against, and recovering from cyberattacks by ensuring best practice is followed at all levels of an organisation.
The latest version of the UK’s Network and Information Systems (NIS) regulations, launched in October 2024, establish clear standards for OESs around the security and resilience of critical IT and OT systems. With the UK Government’s recent expansion of the sectors that fall under the CNI umbrella, a range of new organisations – in sectors such as finance, manufacturing, and data centres - must now achieve compliance with this regulation. Fulfilment of these obligations is best achieved with the support of a trusted technology partner, familiar with converged IT/OT and the current regulatory landscape.
There are multiple aspects to the security of IT/OT environments, including:
- Asset visibility
- Network segmentation
- Identity and access control
- Continuous monitoring
- Secure remote access
- Appropriate governance
- Modernisation of legacy infrastructure
- The implementation of zero-trust principles
- Regular auditing, in line with applicable regulations
A rigorous security framework should take all this into account, along with specialist systems that require a bespoke approach, and be subject to regular review in light of the latest threat intelligence and best practice.
Data sovereignty refers to the governance, control, and legal jurisdiction regarding where data is transferred, processed, and stored. With the rise of regulations such as the US Cloud Act, the growing use of Cloud, SaaS, and AI platforms, and the increasing complexity of global supply chains, it is no longer enough for CNI organisations to simply ensure the physical sovereignty of their data centre environments. Micro and macro views of how data is stored, transferred, and accessed at all times are now essential, particularly in light of an evolving regulatory landscape where noncompliance puts organisations at risk of large fines and potentially irreparable reputational damage.
CNI organisations must establish the appropriate data foundations before beginning any AI initiatives in critical environments. This includes:
- A holistic view of data provenance and quality
- Access controls, based on zero-trust principles
- Effective physical and digital security systems and processes
- Rigorous governance, particularly around the sovereignty of critical data
- Comprehensive risk management about the potential impact of AI on operational environments
The Exponential-e Group brings together more than twenty years of networking expertise and the successful execution of the most complex projects for customers across CNI’s numerous verticals. Our evolving solution portfolio encompasses:
- Connectivity
- Cloud
- Cyber Security
- AI & Data Solutions
- Managed IT
- Support around IT/OT convergence
- Unified Communications and Contact Centre solutions
Our approach to all CNI projects is a highly consultative one, where digital goals are fully aligned with compliance obligations and operational requirements, phasing out legacy systems in favour of secure, scalable, and sovereign platforms that support the seamless delivery of critical services across the whole UK.
We can provide multiple case studies to showcase how this approach has helped organisations across the different CNI verticals expedite their digital transformation journeys and fulfil their compliance requirements.
