
Across the UK's Critical National Infrastructure (CNI), cyber security is now firmly established as a board-level priority, rather than the sole purview of IT and security teams. In response to the increasing range of cyber threats mounted by global bad actors, the Government has implemented an increasingly stringent range of standards around the security and resilience of the systems and data that power the nation's critical services, including the IEC-62443 standard, the NCSC's NIS 2018 directive, CAF V4, and, crucially - the upcoming Cyber Security & Resilience (Network and Information Systems) Bill.
What is the Cyber Security & Resilience Bill?
The Bill updates and expands the existing NIS 2018 regulations, in order to strengthen the UK's overall cyber security posture, particularly with regards to critical services such as energy, water, healthcare, and transport. Key elements of the Bill include:
- Expanded cyber security requirements, in direct response to an increasingly complex global threat landscape, where multiple high-profile attacks on CNI have already affected the availability of mission-critical services.
- Expanding the range of organisations subject to these regulations. The new definition of CNI encompasses fourteen distinct verticals, including utilities, manufacturing, emergency services, data centres, finance, defence, healthcare, and Government organisations - all of whom will be required to achieve and maintain compliance with the Bill.
- More stringent reporting obligations around cyber security incidents, with regard to both speed and detail.
- Increased control and visibility of supply chains, mitigating the risk of bad actors gaining access to critical data and infrastructure via 'backdoor' attacks.
All of this will come with increased penalties for non-compliance, particularly in the event of a security breach, and new powers for regulators regarding investigation, information gathering, enforcement, and remediation.
When does the Cyber Security & Resilience Bill come into force?
The Bill was originally introduced in November 2025 and - at the time of writing, has not yet receive Royal Assent or an official implementation date. However, it has completed its Commons stage, and so is now passing through the House of Lords. With the Government's implementation plans having already been made public and unlikely to significantly change, additional guidance is expected to be issued once Royal Assent has been granted.
How can CNI organisations prepare for the Cyber Security & Resilience Bill?
While we still don't know exactly when the Bill will come into force, it is important to be aware that achieving compliance is likely to take months, which means plans should be initiated at the earliest opportunity, beginning with a comprehensive assessment of all existing systems - both physical and digital - and processes, conducted by a trusted third-party.
This should form the basis of a comprehensive migration plan, not only to fulfil the immediate compliance obligations, but also to ensure best practice is properly embedded at all levels, and security systems and processes are able to adapt to future shifts in the threat landscape. The specifics of this will vary, depending on each organisation's current level of cyber maturity, but are likely to include:
- Conducting regular cyber security and operational resilience assessments.
- Establishing a robust cyber security ecosystem, incorporating zero-trust principles and effective identity and access management (including MFA and PIM), with a UK-based CSOC providing proactive monitoring and alerting.
- Documented processes for incident response and recovery planning, subject to regular review.
- Maintaining clear standards around supply chain risk management, with due diligence, continuous monitoring, and regular security assessments for all third parties.
- Full governance and accountability at the boardroom level, with regular reporting on documented security KPIs and designated executive responsibilities and reporting paths.
For all there will be challenges involved in achieving compliance with the Bill, an effective CNI cyber security posture will be non-negotiable in the years ahead, and so this is the ideal time to review your existing systems and processes, phase out unsecure legacy systems, and maintain the all-important edge as increasingly sophisticated, aggressive threats emerge.
If you are in any way unsure of how the Bill will impact your organisation, get in touch. Our CNI technology specialists will work closely with you to navigate your compliance obligations and ensure your systems and processes always support the highest standards of security and resilience.
Frequently Asked Questions
What is the Cyber Security and Resilience Bill?
The Cyber Security and Resilience (Network and Information Systems) Bill is proposed UK legislation designed to strengthen the cyber security and operational resilience of essential and digital services. It updates and expands the Network and Information Systems Regulations 2018 (NIS Regulations) in response to evolving cyber threats, technology dependencies and supply-chain risks. The Bill introduces changes to the organisations that may fall within scope, cyber incident reporting, regulatory oversight and the management of risks affecting essential services.
Who will be affected by the Cyber Security and Resilience Bill?
The Bill affects organisations already regulated under the UK's NIS framework and extends the regime to additional organisations and services. This includes certain data centres, relevant managed service providers and large load controllers, alongside provisions concerning critical suppliers. Whether an individual organisation is in scope will depend on its activities, sector, size and the definitions and thresholds established by the legislation. Organisations supporting Critical National Infrastructure should assess their potential exposure and dependencies across their supply chains.
What does the Cyber Security and Resilience Bill mean for Critical National Infrastructure?
The Cyber Security and Resilience Bill is particularly relevant to organisations responsible for, or supporting, services on which the UK depends. For Critical National Infrastructure (CNI), the legislation reinforces the need to understand cyber risk across digital and operational environments, strengthen operational resilience, manage third-party dependencies and maintain effective incident detection, response and recovery processes. CNI organisations should consider the Bill as part of their wider cyber security, resilience and governance programmes rather than treating compliance as a standalone exercise.
How does the Cyber Security and Resilience Bill change the NIS Regulations 2018?
The Bill updates and expands the Network and Information Systems Regulations 2018. Proposed changes include extending the regulatory regime to additional organisations, strengthening cyber incident reporting requirements, enhancing regulators' oversight and enforcement capabilities, and introducing measures designed to address systemic and supply-chain cyber risks. The changes reflect the growing dependence of essential services on interconnected digital infrastructure and third-party technology providers.
What are the Cyber Security and Resilience Bill's incident reporting requirements?
The Bill introduces a two-stage reporting process for reportable cyber incidents. Regulated organisations will generally be required to provide an initial notification to their regulator, with the National Cyber Security Centre (NCSC) informed at the same time, within 24 hours of becoming aware of a reportable incident. A fuller report containing additional information will then be required within 72 hours. The Bill also broadens the types of harmful cyber incidents that may need to be reported, including certain incidents with the potential to cause significant impact even where major disruption has not yet occurred.
What does the Cyber Security and Resilience Bill mean for supply-chain cyber security?
The Bill places greater emphasis on cyber risks that can spread through technology providers, managed services and other critical dependencies. This reflects the potential for attackers to compromise a supplier and use that access to affect multiple organisations or essential services. CNI organisations should therefore identify critical suppliers, understand their technology and data dependencies, establish appropriate cyber security requirements and maintain processes for assessing and monitoring third-party risk throughout the supplier lifecycle.
When will the Cyber Security and Resilience Bill come into force?
The Cyber Security and Resilience (Network and Information Systems) Bill has not yet received Royal Assent and therefore does not yet have a final implementation date. The Bill was introduced to Parliament on 12 November 2025 and, following completion of its House of Commons stages, is progressing through the House of Lords. Organisations potentially affected by the legislation should monitor its progress and begin assessing their cyber security and operational resilience rather than waiting for the final implementation timetable before preparing.
How should CNI organisations prepare for the Cyber Security and Resilience Bill?
CNI organisations can begin by assessing whether they are likely to fall within the expanded regulatory regime and reviewing their current cyber security and operational resilience maturity. Preparation should include identifying critical systems and services, mapping digital and operational dependencies, reviewing identity and access controls, assessing supply-chain risk, strengthening monitoring and detection, and testing incident response and recovery processes. Organisations should also establish clear board-level accountability and ensure cyber risk and resilience are incorporated into wider governance and business continuity planning.
What cyber security measures should CNI organisations prioritise?
Priorities will depend on each organisation's risk profile and cyber maturity, but CNI organisations should consider layered security across people, processes, networks, applications and data. This can include Zero Trust principles, identity and access management, multi-factor authentication, privileged access controls, network segmentation, vulnerability management, secure connectivity, continuous monitoring and clearly documented incident response and recovery procedures. A CNI cyber security strategy should also account for operational technology, third-party dependencies and the resilience required to maintain essential services during a cyber incident.
How can Exponential-e help CNI organisations prepare for the Cyber Security and Resilience Bill?
Exponential-e works with organisations responsible for Critical National Infrastructure to assess existing technology environments, identify cyber security and resilience risks and establish practical roadmaps for strengthening their security posture. Our Critical National Infrastructure capabilities bring together secure connectivity, cyber security, cloud, managed IT and communications expertise to help organisations protect critical systems, strengthen operational resilience and prepare for evolving regulatory requirements. Organisations unsure how the Cyber Security and Resilience Bill may affect their operations can engage our CNI technology specialists to review their current environment and priorities.
355 Hits

The seamless delivery of critical services to the public depends on highly secure, resilient connections - not just the networks that interlink IT and OT systems, but the channels of communication that operations depend on. From ensuring citizens are able to speak to the right person to resolve an issue to connecting frontline responders with control centres, and even (in certain cases) keeping physical alarm systems operational, the importance of resilient voice services to the CNI sector cannot be overstated.
However, the way telephony is delivered across the UK is about to fundamentally change…
Following the initial announcement in 2018, the legacy PSTN and ISDN connections that traditionally formed the bedrock of the UK's voice services have been gradually phased out in favour of IP-based alternatives, including VoIP, SoGEA, and FTTP, with the final switch-off scheduled for January 31st, 2027. As a result, organisations still utilising those connections must find an alternative and make the transition before the cut-off date.
For CNI Organisation, it is essential that this transition is completed well in advance of the switch-off, as any disruption to critical services can have potentially serious consequences, ranging from fines for non-compliance to - in the most serious cases, loss of life. This is codified in the Government's Telecoms Modernisation: Critical National Infrastructure Charter paper, which requires CNI organisations to work closely with their communication providers to ensure any potential disruption is avoided.
However, the move to IP-based connections offers a unique opportunity to further optimise the resilience and availability of the UK's critical services, ensuring channels of communication always remain open and of the very highest quality, even in the most remote areas. The inherent scalability of IP-based connectivity is a major advantage for CNI, ensuring cost control can be maintained as organisations expand their operations into new locations, with no need to purchase new hardware.
As a trusted technology partner for numerous organisations across the UK's CNI sectors, the Exponential-e Group is already providing hands-on support throughout this shift, not only helping organisations select the ideal solution for their applications, but also ensure a seamless transition that avoids any operational disruption and ensures full compliance with all applicable regulations is maintained.
If you are in any way concerned about how the PSTN switch off will impact your operations, contact us to review the available options and establish which will best support your communication needs and establish a roadmap for the required migration. Working together, we will ensure telephony continues to remain a fundamental part of your overall operational efficiency, helping maintain public confidence in the UK's ever-evolving CNI.

Frequently Asked Questions
When is the PSTN switch-off in the UK?
The UK's legacy Public Switched Telephone Network (PSTN) is scheduled to be retired on 31 January 2027. Organisations still using PSTN or ISDN-based services should identify affected connections and migrate them to suitable digital alternatives before the deadline. Exponential-e provides PSTN switch-off migration support to help organisations assess their existing services and establish a clear transition plan.
What does the PSTN switch-off mean for Critical National Infrastructure?
For Critical National Infrastructure (CNI) organisations, the PSTN switch-off is more than a telephony upgrade. Legacy connections can support operational services, alarms, monitoring systems and communications between sites, control centres and frontline teams. Any unidentified dependency could create an operational resilience risk when legacy services are withdrawn. Organisations responsible for Critical National Infrastructure should therefore identify dependencies and establish migration, resilience and testing plans well before the final switch-off.
Which CNI systems could still rely on PSTN or ISDN?
PSTN and ISDN connections may support more than traditional telephone handsets. Depending on the organisation and its estate, legacy lines can be connected to alarm systems, lift emergency phones, security systems, monitoring equipment, telemetry, intercoms, fax services and other operational devices. CNI organisations should conduct an estate-wide audit to identify legacy connections and understand which critical services depend on them before beginning migration.
What will replace PSTN services after January 2027?
Traditional PSTN and ISDN services are being replaced by digital and IP-based communications delivered over modern connectivity. The appropriate replacement will depend on the application, location, existing equipment, availability requirements and resilience needs. Technologies can include IP-based voice services delivered over fibre and other digital access technologies. Organisations should assess each legacy service individually rather than assume that a single replacement technology will be suitable across their entire estate. Explore Exponential-e's Connectivity Services and PSTN migration options.
Will analogue alarms and monitoring systems work after the PSTN switch-off?
Not necessarily. Some analogue alarms, monitoring systems and other specialist devices were designed to communicate over traditional PSTN lines and may not operate correctly when connected to an IP-based service without modification, replacement or an appropriate adapter. Organisations should identify these devices, confirm compatibility with the equipment manufacturer or service provider, and test migrated services before the existing connection is withdrawn.
How can CNI organisations identify their PSTN dependencies?
CNI organisations should conduct a structured audit of their communications estate, covering known telephone services as well as alarms, telemetry, monitoring equipment, security systems, emergency lines and other devices that may use analogue connectivity. Each connection should be mapped to the service it supports, its location, operational criticality and required resilience. This creates a clear migration inventory and helps prioritise critical services ahead of the PSTN switch-off.
What are the risks of delaying PSTN migration?
Delaying migration reduces the time available to discover hidden dependencies, confirm equipment compatibility, design replacement services, coordinate suppliers and test resilience before legacy connections are withdrawn. For CNI organisations, disruption could affect critical communications or operational systems, so migration should be treated as an operational resilience programme rather than a last-minute telephony replacement. Exponential-e's PSTN switch-off specialists can support planning and migration ahead of the 2027 deadline.
How can CNI organisations maintain communications during a power or network outage?
IP-based communications depend on the underlying network and powered equipment, so resilience should be designed into the complete service rather than considered only at the telephony layer. Depending on operational requirements, this can include resilient connectivity, diverse network paths, backup power, automatic failover and alternative communications technologies. Exponential-e's Connectivity Services are designed to support secure, resilient communications across business-critical environments.
How should CNI organisations plan a PSTN migration?
A CNI PSTN migration should begin with discovery of all legacy connections and the services that depend on them. Organisations can then assess operational criticality, confirm equipment compatibility, select suitable digital alternatives, design appropriate resilience, migrate services in controlled phases and test them before retiring existing connections. Maintaining an accurate record of dependencies and completed migrations is particularly important across complex, multi-site CNI estates.
How can Exponential-e support CNI organisations with the PSTN switch-off?
Exponential-e can help organisations assess existing PSTN and ISDN dependencies, identify appropriate digital alternatives and establish a migration roadmap designed to minimise operational disruption. Our wider Critical National Infrastructure capabilities combine secure connectivity, communications and technology expertise to support organisations operating critical services across the UK. Organisations preparing for the deadline can also explore our dedicated PSTN switch-off support.
331 Hits

With a diverse range of SaaS and Cloud platforms now firmly established across corporate workflows and AI continuing to reveal its true potential in the workplace, the demand for highly secure, resilient, and available connectivity has never been higher. When the foundational connectivity that connects organisations to their colleagues, partners, and customers becomes unavailable, it's more than an inconvenience. Even the shortest periods of downtime can result in serious financial, operational, and reputational consequences, particularly when we consider the increasingly stringent compliance landscape around the availability of critical services.
London experienced this first-hand in late 2025, when an underground fire at Holborn led to around 2,000 people being evacuated and outages lasting as long as fifteen days. Businesses relying on single circuits for their networking were the most heavily affected, as repairs were not possible until the fires were contained.
This highlights the value of true resilience when it comes to the connectivity businesses depend on. By 'true resilience', we don't just mean the ability to detect and mitigate security issues and operational risks (as important as that is), but also the ability to recover from major external disruptions like the Holborn fire that no-one could have predicted.
As with most aspects of digital infrastructure, redundancy is key here. There should be no single point of failure in any area of an organisation's foundational network. For this reason, many organisations have opted for carrier diversity across their network design - the practice of utilising connections from multiple providers with failover measures in place to maintain continuity in the event of any disruption.
This approach is certainly effective much of the time, but it has its limitations, as many organisations affected by the Holborn outages found to their cost. Often, connections from different providers are deployed along the same routes under the streets, which means that an unexpected disruption can affect several simultaneously, leaving organisations who depend on them without their networks and unable to do business.
In addition to carrier diversity, geographical diversity should be factored into network design, with redundant connections deployed along dispersed routes as much as possible. Ideally, network providers should be able to provide this as part of the proposed network design, which will allow multiple suppliers to be consolidated, for better efficiency and cost control.
Exponential-e launched, and continues to develop -our EXPO.e Networks platform with this new standard of resilience in mind. From our initial deployments through to our most recent initiatives across South London locations, when deploying high-quality fibre into new premises, we always utilise full route diversity, based on dispersed entry points for maximum service resilience.
Looking further ahead, our perspective on network resilience needs to evolve, considering both a greater range of potential disruptions and the higher standard of performance and availability demanded by the modern, interconnected workforce. This reflects the shifting role of connectivity, as organisations increasingly view it as a powerful driver of innovation and growth rather than a simple operational expense, particularly as SaaS, Cloud, and AI platforms further establish themselves as critical business tools.
If you're keen to take the next step of your own connectivity journey, just get in touch. Our network specialists will work closely with you to design and deliver scalable, futureproof, and highly resilient connections that not only fulfil your immediate networking requirements, but provide the ideal foundation for your wider IT ecosystem as it evolves.
Frequently Asked Questions
Does carrier diversity guarantee network resilience?
No. Using multiple network carriers can reduce dependency on a single provider, but it does not necessarily provide full network resilience. Connections supplied by different carriers may still share the same underlying fibre routes, ducts, exchanges or building entry points. A disruption affecting that shared infrastructure could therefore impact multiple connections simultaneously.
What is the difference between carrier diversity and route diversity?
Carrier diversity uses connectivity services from different network providers, while route diversity ensures those connections follow physically separate geographical paths. Combining carrier diversity with geographical route diversity can help organisations reduce shared points of failure and build more resilient network infrastructure.
Why is geographical route diversity important?
Geographical route diversity helps reduce the likelihood that a single physical incident will affect every network connection serving an organisation. By using physically separated routes and, where possible, diverse building entry points, organisations can maintain connectivity when one route is disrupted by construction damage, flooding, utility failure or another localised incident.
What is a single point of failure in a network?
A single point of failure is a component, route or location whose failure could interrupt a wider network service. Shared fibre routes, ducts, exchanges, network equipment and building entry points can all create potential single points of failure. Identifying and removing these dependencies is an important part of designing a resilient network.
How can businesses improve network resilience?
Businesses can improve network resilience by combining redundant connectivity, carrier diversity, geographically diverse fibre routes, diverse building entry points and effective failover. Network designs should also be regularly reviewed to identify shared physical dependencies and potential single points of failure as an organisation's connectivity requirements evolve.
Can two different network providers use the same fibre route?
Yes. Connections purchased from different network providers can still share underlying ducts, fibre routes, exchanges or other physical infrastructure. This means using two carriers does not automatically provide geographical diversity. Organisations should establish how their connections are physically routed when assessing the resilience of their network design.
316 Hits

Navigating compliance for the UK's Utilities sector
For the UK's Utilities sector, compliance is not simply an annual box-ticking exercise. It's a foundational element of secure, seamless operations that ensure these critical services are readily available to citizens across the country, 24 / 7. However, as the range of potential threats and disruptions the sector must identify and mitigate has expanded, so too have organisations' regulatory obligations, meaning achieving and maintaining compliance can often seem an onerous burden.
Key regulations that must be considered at the time of writing include:
- NIS (2018). The latest iteration of a globally recognised framework for the physical and digital security of network and information systems.
- IEC-62443. An evolving framework for optimising the security of critical infrastructure, encompassing both design and operations.
- The Cyber Security and Resilience Bill. An expansion of the NIS (2018) regulations, currently moving through the House of Lords, that will make additional companies subject to the regulation, while bringing in more stringent requirements around incident reporting and transparency and imposing more severe financial penalties for non-compliance (as much as £17m or 4% of annual revenue).
This increasingly rigorous regulatory landscape is largely in response to the increasing threat posed by cyber attacks conducted by both domestic and international bad actors. The highly interconnected nature of the Utilities sector's underlying infrastructure, with IT and OT systems increasingly converged, has made these systems a highly attractive target for those looking to compromise our nation's critical national infrastructure, with 77% of Utilities providers reporting attack in the first half of 2026, largely focused on legacy technologies, email platforms, and servers1.
In this heightened state of threat, the importance of full compliance with all applicable regulations cannot be overstated.
Simplifying the compliance journey has been a key area of Vysiion's work across numerous sectors, particularly Operators of Essential Services (OESs), since our inception. We not only operate according to these recognised standards ourselves, but also work closely with our customers to help them do the same. This goes beyond simply passing the annual audit - it means embedding the underlying principles in all aspects of companies' day-to-day operations, ensuring current best practice is understood and applied at all levels.
This, in turn, will build public confidence in the Utilities sector as a whole, avoiding the risk of costly and damaging security breaches that could, in extreme cases - lead to loss of life.
If you are in any way concerned about your own compliance journey, do not hesitate to get in touch. We will ensure you are fully aware of which regulations apply to your organisation, then work closely with you throughout the audit processes, drawing on proven methodologies and our deep understanding of IT / OT systems across the Utilities sector, making the whole process seamless and successful. In this way, a whole new standard of physical and digital security will become firmly embedded in your company culture, allowing you to maintain that all-important edge against the most sophisticated, aggressive threats and ensure the UK's critical service are always available.

Frequently Asked Questions
What cyber security regulations apply to UK Utilities?
UK Utilities organisations may be subject to the Network and Information Systems Regulations 2018, particularly where they are designated as Operators of Essential Services. Organisations should also consider relevant sector guidance and recognised standards, including the IEC 62443 series for industrial automation and control systems. The UK regulatory landscape is also evolving through proposed reforms intended to strengthen cyber security and resilience requirements for essential and digital services.
What are the NIS Regulations 2018?
The Network and Information Systems Regulations 2018 establish cyber security and incident management requirements for organisations that provide essential and certain digital services in the UK. They are designed to improve the security and resilience of the network and information systems that support essential services.
What is IEC 62443?
IEC 62443 is a series of international cyber security standards for industrial automation and control systems. It provides requirements and processes for designing, operating and maintaining secure industrial environments across their lifecycle, helping organisations strengthen cyber security across operational technology, IT and industrial control systems.
What does the Cyber Security and Resilience Bill mean for Utilities?
The Cyber Security and Resilience Bill is intended to reform and expand the UK's existing cyber security regulatory framework. For Utilities and other organisations operating essential services, the changes are expected to broaden regulatory coverage and strengthen requirements around cyber risk management, resilience, incident reporting and supply chain security.
Why is operational technology cyber security important for Utilities?
Utilities rely on operational technology to monitor and control physical infrastructure and essential processes. As OT becomes increasingly connected to enterprise IT, remote access services and third-party systems, the potential attack surface grows. A successful cyber attack can therefore affect not only data and systems, but also service availability, operational safety and critical infrastructure.
How does IT and OT convergence increase cyber risk?
Connecting IT and OT environments can improve visibility, automation and operational efficiency, but it can also create new routes into systems that were historically isolated. Legacy technology, insecure connections, third-party access and weak network boundaries can increase the risk of attackers moving between environments, making secure architecture, segmentation and monitoring increasingly important.
How can Utilities improve cyber resilience?
Utilities can improve cyber resilience by maintaining an accurate understanding of their IT and OT assets, limiting unnecessary connectivity, strengthening network boundaries, segmenting critical systems, controlling third-party access and continuously monitoring network activity. Organisations should also maintain tested incident response, isolation and recovery processes so essential services can continue operating during disruption.
Is passing a cyber security audit enough to remain compliant?
No. Effective compliance should be treated as an ongoing operational discipline rather than an annual audit exercise. Utilities organisations need to continuously assess cyber risk, maintain security controls, manage vulnerabilities, monitor their environments and adapt their approach as regulations, technologies and threats evolve.
How can Vysiion support Utilities cyber security and compliance?
Vysiion works with Utilities and Critical National Infrastructure organisations to strengthen cyber security and resilience across complex IT and OT environments. Our specialists can help organisations understand applicable requirements, assess their current security posture, prepare for audits and implement secure infrastructure, connectivity, monitoring and operational technology security solutions aligned with their wider compliance and resilience objectives.
1151 Hits

The way we connect, communicate, and collaborate continues to evolve, with hybrid working now firmly established across the public and private sectors, and SaaS adoption increasing, as our understanding of these new workflows improves. At the time of writing, it is anticipated that 90% of organisations will rely primarily on SaaS platforms by 2030 - a completely new model of enterprise infrastructure that will free employees of their traditional ties to specific locations and devices.
However, as with any period of intensive digital transformation, potential security vulnerabilities must be given careful consideration. Indeed, 66% of organisations already cite the security of SaaS platforms as their biggest challenge – concerns compounded by a number of recent high-profile incidents where bad actors have utilised security vulnerabilities in SaaS platforms (some caused by misconfiguration, others by simple human error) to gain access to corporations' critical data.
Traditional security ecosystems are typically based on building security around the network and were never designed to accommodate secure remote access at scale. As a result, with many organisations forced to rapidly pivot to hybrid working throughout the COVID-19 lockdowns, security has often become fragmented across multiple users, devices, and locations. Not only does this represent a significant increase in operational overheads, maintaining numerous heavily siloed platforms make the consistent application of corporate security policies and visibility of user devices extremely complex and time-consuming to maintain. As a result, it is far too easy for security vulnerabilities to go undetected until a breach occurs, particularly when we consider the risk of 'shadow IT', where employees are using Cloud and SaaS platforms that have not been validated by corporate security teams as part of their day-to-day work.
While it may be possible to implement security solutions on a case-by-case basis, i.e. the use of VPNs, this will not, ultimately, be sustainable. Not only will it exacerbate the concerns highlighted above, it will also introduce additional latency and complexity that is unacceptable at a time when employees expect critical platforms to always be available and always offer the highest standards of performance.
Taking all these concerns into account, it is clear that we need to rethink the way we design, implement, and manage network security, ensuring policies are applied consistently and correctly for all users and all devices, wherever they are connecting from. Rather than deploying multiple security solutions across a pre-existing network infrastructure, a unified model of network security is required - one that can accommodate the diverse nature of SaaS platforms and the dynamic nature of modern workflows.
FortiSASE offers a single, fully centralised answer to these concerns. A Cloud-based Security Service Edge (SSE) solution, built on Fortinet's best-in-class security platform and delivered as a fully managed service by Exponential-e, FortiSASE intelligently automates that application of corporate security policies across users, devices, and locations, without the complexity of traditional network controls. This way, full control and visibility of all network traffic can be maintained, without compromising the performance and availability of approved SaaS applications.
If you are in any way frustrated by the performance of your critical applications or concerned about the security of your network, get in touch, and our specialists will work closely with you to phase out your legacy systems in favour of next-gen solutions that fully support your specific workflows.
1394 Hits

Legacy connectivity technologies, particularly the PSTN and ISDN, have been the foundation of many organisations' communications for some years now, but have increasingly shown their limitations, with aging copper networking increasingly prone to faults and unable to maintaining the resilience and availability that modern voice, email, and video platforms demand. Indeed, PSTN incidents rose by 45% in 2024 alone, with 192 million hours of service lost between 2024 and 2025 - all of which had a serious financial, operational, and reputational impact on the organisations affected1.
In light of this shift, a full switch-off of the PSTN network has been in progress for several years now, and will be concluded by January 2027, after which any organisations that have not migrated to alternative systems will be without voice and broadband services.
Fortunately, all-IP connections offer considerable advantages over these legacy technologies, and so this change represents an ideal opportunity to optimise and futureproof the performance and availability of your voice and broadband services.
What is the PSTN switch-off?
In 2018, BT Openreach announced the long-term plan to transition the whole of the UK from PSTN to IP for all voice calls. To this end, as of September 2023, no new PSTN or ISDN lines will be deployed, in preparation for 2027, when the remaining ones would be permanently switched off. At the time of writing, a stop-sell has been placed on multiple voice products built on these services, meaning existing ones will initially remain in place, but new ones will be withdrawn from sale.
For organisations planning to transfer to new solutions before stop-sells are implemented in their active regions, it is important to be aware that not all services will necessarily be available. For example, in regions where the FTTP priority exchange is in place and FTTP is available at premise level, this is the only service that they will be able to utilise. Outside of these regions, other transitional solutions, such as SoGEA and SoADSL - may be available. All this must be factored into organisations' migration plans.
Why are numerous organisations already embracing IP-based connectivity?
IP technology allows broadband connectivity and compatible digital voice services to operate over the same data network, removing the need for legacy PSTN connectivity. These services can be delivered over a broadband connection, such as FTTP, SoADSL or SoGEA, or over an ethernet service (although the underlying connection does not provide a traditional dial tone as standard).
This will open up a whole new era of quality and resilience in the way voice and broadband services are delivered across the country, provided organisations are aware of the impending change and plan accordingly. This will involve working closely with a trusted connectivity partner to not only migrate to a new service, but ensure the solution chosen will provide the required performance, resilience, and scalability, while retaining cost control.
IP technology allows broadband connectivity and compatible digital voice services to operate over the same data network, removing the need for legacy PSTN connectivity. These services can be delivered over a broadband connection, such as FTTP, SoADSL or SoGEA, or over an Ethernet service. However, the underlying connection does not provide a traditional dial tone as standard.
How Exponential-e can help
Exponential-e is already working closely with organisations across multiple sectors to prepare for the switch-off, providing them with a range of migration options that will not only ensure disruption is minimised, but open up new opportunities to reduce costs, while optimising resilience and service quality.
There are a range of ways these benefits can be unlocked, depending on where you, your teams, and your customers are active, the services you utilise each day, and whether you currently utilise copper wiring for other services. It is important to bear in mind that not every available solution will necessarily be the right fit for every organisation, but our teams are here to guide you.
Exponential-e's portfolio of services - including, FTTP, SoGEA, SoADSL, and VoIP services - was designed to be truly vendor-agnostic for precisely this reason. We work with multiple carriers to ensure our customers and their end users enjoy the best possible coverage across the entire UK. As with every aspect of our services, our approach is a consultative one, with our own experts working closely with customers' teams to develop a robust migration plan to mitigate the impact of the switch-off and ensure a smooth transition to your ideal IP-based service.
Do not hesitate to contact us to discuss your voice and connectivity requirements and how the impending switch-off will affect you.

Frequently Asked Questions
What is the PSTN switch-off?
The PSTN switch-off is the UK's nationwide retirement of the Public Switched Telephone Network (PSTN) and ISDN services. By January 2027, all organisations will need to use IP-based voice and broadband services instead of legacy copper telephone lines.
When is the PSTN switch-off?
The UK PSTN network will be permanently switched off in January 2027. Organisations that have not migrated to IP-based connectivity before this deadline risk losing access to traditional voice and broadband services.
Will my business phones stop working after the switch-off?
If your organisation still relies on PSTN or ISDN services without migrating to an IP-based solution, traditional business phone services may no longer function once the network is switched off.
What technologies will replace PSTN?
Modern alternatives include FTTP, Ethernet, SoGEA, SoADSL, VoIP and Cloud-based communications. These services provide greater resilience, improved call quality, scalability and support for hybrid working.
What are the benefits of migrating before January 2027?
Migrating early helps avoid service disruption, improves business resilience, enhances voice quality, reduces operational costs and provides sufficient time to test and optimise your new connectivity before the deadline.
Will I need full fibre broadband?
Not necessarily. While FTTP provides the highest performance where available, organisations may also benefit from SoGEA, SoADSL or dedicated Ethernet services depending on their location, infrastructure and business requirements.
What other business services could be affected by the PSTN switch-off?
Many legacy services rely on PSTN connections, including lift emergency phones, alarm systems, payment terminals, telemetry devices and some building management systems. These should all be assessed as part of your migration planning.
How can Exponential-e help with the PSTN migration?
Exponential-e provides a consultative, vendor-agnostic approach to migration, offering FTTP, SoGEA, SoADSL, Ethernet and VoIP solutions through multiple UK carriers. Our experts work with your organisation to create a tailored migration strategy that minimises disruption while improving resilience, scalability and long-term performance.
1. BT Wholesale
1115 Hits

There's no doubt that times are tough for the great British pub, with 161 closures reported across the country in the first quarter of this year alone1, combined with £322.5m of new employment costs to consider since the last autumn budget and the rising cost of national insurance2. At the same time, we're seeing a widespread cultural shift, particularly amongst the younger generations.
About a third of young people have reported cutting back their alcohol intake over the past twelve months, typically citing budget and health as driving factors (or just wanting to drink less!)3. But despite this shift, the sector remains valued at £24.9bn (with this expected to rise to £25.7bn by 2028)4, and post-work drinks remaining a consistent source of revenue, and pub meals remaining popular despite an overall drop in dining out5.
However, just as we saw during COVID lockdowns, the sector never fails to demonstrate its resilience and creativity when challenged. In my role at Exponential-e, I regularly speak to pub owners and managers (purely in a professional capacity!) who're eager to build on the lessons learned throughout lockdowns and the success of the first digital transformation initiatives that resulted. And hopefully England can go all the way and give the pub industry a revenue boost!
So, I feel we can confidently say that one of our most beloved national institutions isn't going anywhere, but it's not going to be enough to assume drinking and dining habits will remain the same, or that patrons' expectations around the overall pub experience are the same as they were just a few years ago. Specifically, here are the four ways I would anticipate the sector evolving in the years ahead…
Operational efficiency will be a top priority
Rising labour costs, particularly the increase in both National Insurance and the National Living Wage - mean the sector as a whole is having to do more with less, ensuring available staff can continue delivering exceptional service without putting their own health and wellbeing at risk. A detailed answer to these challenges lies outside the scope of this article, but when the highest level of operational efficiency is required, technology definitely has a role to play by reducing waste, automating routine processes and administrative tasks, and providing streams of real-time staffing information that support better decision-making at the micro and macro levels. All of this will ultimately lead to tangible cost savings that can be reinvested in the patron experience.
Patrons' expectations will continue evolving
Along with the shift in drinking habits that we touched on earlier, it's also important that we're cognisant of the different ways in which patrons access services and information. We very much live in an interconnected society, with younger generations preferring everything to be readily accessible through their smart devices. However, the pub sector is already very much ahead of the game here, having rolled out app-based service at scale during COVID. This means we have a strong foundation to build on, gaining a better understanding of patrons' ordering habits and utilising this to tailor services, menus, and marketing activities accordingly.
Infrastructure must be designed for scale
Far too many pubs that are part of chains or groups are still relying on fragmented, multi-vendor environments when it comes to connectivity, systems, and communications. Beyond the considerable ongoing expense this presents, it puts far too many pubs at risk of being unable to trade if their local infrastructure goes down. In our post-cash society, if you can't take card payments, you can't do business, which impacts both your profits and your reputation.
Furthermore, when central offices must manage hundreds of sites across the country, all utilising their own legacy infrastructure, it creates an unacceptable operational burden.
For this reason, we are seeing an increasing number of chains and groups accelerating their long-term digital transformation plans, working with trusted technology partners to phase out siloed legacy systems in favour of fully consolidated infrastructure that provides full control and visibility of all sites, combined with in-built redundancy to ensure trade is never disrupted by an outage, even in particularly remote locations.
Security must be inherent in the design
Of course, as pubs embrace the next generation of interconnected infrastructure, their tech-savvy patrons expect them to take action to ensure their personal data remains secure, before, during, and after each visit. Security ecosystems must take into account payment card data, guest WiFi networks, loyalty databases, employee records, and much more. This is not negotiable - the regulatory landscape is increasingly stringent about the way customer data is handled at every touchpoint, and the penalties for non-compliance are steep.
We just have to look at the number of organisations who've been left unable to trade and suffered potentially irreparable reputational damage after falling victim to cyber attacks in recent years to see how serious this situation is. Digital transformation initiatives cannot afford to treat security as a bolt-on. Instead, it must be inherent in the design of all infrastructure, with corporate security policies automatically applied wherever possible and regular training provided for all staff.
From pouring pints to delivering experiences
While there are certainly challenges ahead, the UK's pubs are well-placed to weather them, ensuring these spaces remain a beloved social hub for future generations. While younger people are certainly drinking less, quality experiences never go out of fashion, and the pubs that will continue to thrive are the ones who embrace this fact, looking for new ways to bring people together in unique environments.
While it may feel contradictory to talk about digital transformation at the same time as human experiences, automating routine processes and opening new channels for interaction with patrons is all about ensuring staff are free to focus on the personal touches that turn first-time patrons into loyal, repeat ones. A perfect example of what can achieved when people and technology come together!
If you're keen to accelerate your own digital transformation after reading this, let's arrange a conversation.

Frequently Asked Questions
How can digital transformation help UK pubs?
Digital transformation can help pubs improve operational efficiency, reduce waste, automate routine tasks, support cashless payments and create more personalised customer experiences.
Why is connectivity important for modern pubs?
Reliable Connectivity supports payment systems, app-based ordering, guest WiFi, loyalty platforms and operational systems, helping pubs continue trading without disruption.
How can pubs improve operational efficiency with technology?
Pubs can use technology to automate administrative tasks, monitor staffing levels, reduce waste, analyse customer behaviour and make faster decisions across single sites or multi-site estates.
Why does infrastructure need to be designed for scale?
Scalable infrastructure helps pub groups consolidate fragmented systems, improve visibility across multiple sites and maintain service continuity during busy trading periods or local outages.
How can pubs protect customer data?
Pubs can protect customer data through Cyber Security, secure payment infrastructure, protected guest WiFi, access controls and security policies applied consistently across all digital systems.
Why is security important for hospitality digital transformation?
Security must be built into hospitality infrastructure from the start to protect payment data, loyalty databases, employee records and guest services from cyber threats and compliance risks.
How are customer expectations changing in the pub sector?
Customers increasingly expect convenient digital services, app-based ordering, reliable WiFi, personalised offers and seamless experiences that combine traditional hospitality with modern technology.
What technology should pub groups prioritise?
Pub groups should prioritise resilient Connectivity, secure payment systems, Cloud Services, Cyber Security, guest WiFi, analytics platforms and systems that provide central visibility across all sites.
1. British pubs closing at a rate of almost two per day in 2026 - BBC News
2. Why Are UK Pubs Closing in 2026? The Employment Answer
3. Why are one in three Brits drinking less alcohol in 2026?
4. UK Pub Industry Outlook 2026: Costs Rise but World Cup Could Boost Sales | Morningstar UK
5. Pubs under pressure as eating out growth slows in 2026
987 Hits
In today's interconnected society, our data is a fundamental part of our personal and professional lives, informing everything from the way we communicate and collaborate with our colleagues to the way we do our weekly shop. Seamless, secure flows of data have transformed the way we access many critical services and helped bring a rich vein of new innovations to market, but as with any period of intensive technological evolution, these benefits have come at a price…
In a highly unpredictable geopolitical landscape, the growing volumes of data created, stored, and transferred by public sector and enterprise organisations present an extremely attractive target for bad actors, as does corporations' intellectual property and citizens' personal data. It's unsurprising that organisations across the public and private sectors are treating the continued integrity of their data as a critical priority - not only to avoid the financial and reputational consequences of a breach, but also to provide customers and prospects with assurance that their critical data will always be protected, both at rest and in transit.
Data sovereignty is a key part of this journey, by which we mean, in the broadest sense - guarantees over the geographical locations in which data may be stored. Most technology providers will already have such guarantees in place, typically involving the location of their hosting environments. However, with the now near-ubiquity of Cloud platforms and the growing complexity of security and compliance, the nature of true data sovereignty is no longer so clear.
With this in mind, consider the following questions when evaluating Cloud providers…
Is your Cloud provider fully incorporated in your desired location? While they may maintain hosting environments there, can they say the same for the Cloud platforms you will be utilising, particularly if they are operating as part of a larger umbrella company? If not, you cannot guarantee that your data will remain within the country when in transit, which may lead to compliance and security issues
Will they maintain full jurisdictional control of all data? Related to the above point, with several governments having now implemented regulations that grant them access to data stored in Cloud platforms (e.g. the US Cloud Act), providers must be able to guarantee that customer data will never be subject to such overreach. This is especially critical for any sort of public sector data, particularly Government and defence.
Can they specify which personnel have access to their Cloud platforms? Again, all engineers who will be maintaining the Cloud platform and acting on behalf of customers must be based in their sovereign nation, with the appropriate clearances and certifications in place.
Does their data sovereignty extend to their disaster recovery and business continuity practices? The sovereignty of data centres must extend to back-up environments, which must also be located in the designated geographical region, with air gapping, data encryption, and zero-trust security measures utilised as appropriate, and all of this subject to annual audit.
This is why Exponential-e has continued to develop our ability to guarantee true data sovereignty, in direct response to the evolving digital and geopolitical landscapes. To this end, we were recently certified as a VMware Sovereign Partner, reflecting our ability to provide complete assurance around the sovereignty and control of digital assets. The are multiple dimensions to this, including our hosting facilities, support, management, regional jurisdictions, security clearances, and ability to deliver complementary services, such as Bring Your own Key (BYoK) and both shared and dedicated Cloud environments. As a proudly UK-based company for more than twenty years, our full range of solutions is designed with true sovereignty inherent in the design – something we continue to develop in response to the latest regulations, geopolitical shifts, and security challenges.
If you are in any way concerned about the sovereignty of your data and your key platforms, do not hesitate to reach out to our team, who will guide you through these challenges, ensuring you can continue your Cloud journey with complete peace of mind.

Expert Insights
-
- Cloud
-
- Cross Sector
-
- Thought Leadership
1557 Hits

In the space of just a few years, AI has moved from the realms of science fiction to the forefront of many organisations' digital transformation strategies. But when global bad actors will seize on any opportunity to access enterprise infrastructure, it is essential that in the rush to train the new algorithms and unlock all the promised benefits, we do not put our sensitive data at risk.
We've spoken before about the increasing importance of true data sovereignty, and maintaining full control and visibility over how our data is stored, managed, and utilised. As AI adoption is increasingly widespread - from content creation to data analysis, customer contact, and digital pathology, such concerns will only increase, and so it is essential that we establish a clear understanding of how the security and sovereignty of our critical data will be impacted.
However, standing still is not an option. Many organisations are falling foul of 'shadow AI', where employees' ill-informed use of public AI platforms at work has impacted the security and sovereignty of their sensitive data. Indeed, in April 2024, a survey of CISOs found that one in five UK organisations had their sensitive data exposed by employees' use of GenAI, with 75% of respondents considering such platforms a greater security risk than external threats1.
To complicate matters, there is still a severe lack of transparency around how GenAI companies utilise users' data to train their models, and no guarantee that they will take organisations' security and compliance practices into account as the race for industry dominance continues. GenAI providers are corporations and have their own interests firmly at heart. In other words, once your employees have allowed a platform access to your data - however well-intentioned the application may be, you have no way of knowing how it will then be utilised, or even whether it will remain within your region.
These concerns are exacerbated by over-reaching regulations such as the US Cloud Act (2018), which all US-based firms are subject to, requiring them to grant the Government access to their data on request, regardless of where their physical servers are located. This, of course, creates considerable risk of conflict with data protection regulations, such as the GDPR, and undermines the sovereignty of organisations' critical data. In a worst-case scenario, this may lead to costly fines and reputational damage if organisations are found to have inadvertently breached their compliance with applicable data protection regulations.
So, whether you are planning on embedding AI at scale or using a softer touch, a clear strategy around AI and data security and governance, at both the micro and macro levels, must be established and documented. This should then inform everything from large-scale technology investments to day-to-day working practices, with designated individuals responsible for ensuring these standards are adhered to and regular training provided to employees to ensure they understand their individual responsibilities.
Taking these principles to their logical conclusion, there's a strong case to be made for bringing AI to your data, rather than the other way round. Instead of putting your trust in a single provider, who may not share or be able to accommodate your security and sovereignty goals, you should establish your own 'toolbox' of solutions that have been designed with specific data protection practices in mind or even developing them in-house if they do not currently exist.
While work still needs to be done establishing clear standards of best practice around AI's implementation across enterprise environments, I would anticipate that this will soon become non-negotiable for GenAI providers, as organisations must contend with increasingly stringent compliance obligations (particularly those operating within the CNI sectors) and end users demand reassurance that the integrity of their data will be maintained. If providers are willing and able to collaborate with their end users to this end, we will not only see an increase uptake of these technologies but also ensure the UK's critical data will remain secure in an increasingly turbulent geopolitical landscape.
Ultimately, the message is clear - do not leave any of this to chance. For this reason, Exponential-e offers a suite of hands-on workshops, where our experts will work closely to establish how and where AI can offer the most benefit to your organisation, determine your current level of AI maturity, and develop an effective roadmap for its implementation - all while maintaining the most rigorous security, governance, and compliance.
Frequently Asked Questions
What is sovereign AI?
Sovereign AI enables organisations to maintain control over how data is stored, processed, governed and secured, often within a specific jurisdiction.
Why is sovereign AI important?
It helps protect sensitive data, reduce compliance risk and prevent unintended use of information by third-party AI providers.
What are the risks of public generative AI?
Risks include sensitive data leakage, poor governance, unclear residency, compliance breaches and shadow AI usage.
What is shadow AI?
Shadow AI refers to employees using unauthorised AI tools without governance, increasing security and compliance risks.
Can organisations use AI securely?
Yes. Private or sovereign AI environments, governance controls and secure data access models can enable safe adoption.
How does the US Cloud Act affect sovereignty?
It may allow US providers to comply with government data requests regardless of where information is physically stored.
Is sovereign AI required for GDPR?
No, but it can reduce risk through stronger control over location, access, governance and processing.
How should CNI organisations adopt AI?
Through secure, governed environments that prioritise resilience, sovereignty and sector-specific compliance.
What does a sovereign AI strategy include?
- Governance policies.
- Approved environments.
- Access controls.
- Compliance requirements.
- Training and monitoring.
How can organisations assess AI readiness?
Assess maturity, governance, security, use cases and compliance requirements to build a balanced roadmap.

1. Fifth of CISOs Admit Staff Leaked Data Via GenAI - Infosecurity Magazine
1584 Hits

Mathematician Clive Humby said in 2006 that "Data is the new oil". Twenty years on, he has been proven right in ways he could never have anticipated. The increasing integration of physical and digital systems, followed by the rapid rise of Artificial Intelligence (AI), means that data is now very much a national resource - one that's not only driving growth across both the public and private sectors, but also transforming the way critical services are delivered, enhancing our collective wellbeing and quality of life.
However, in the rush to achieve all the outcomes promised in AI's earliest days, too many organisations find themselves limited by the foundational infrastructure. Legacy systems were simply not designed with such sophisticated, resource-intensive applications in mind, and so find themselves held back by inconsistent capacity and availability, disparate systems delivered by multiple suppliers (who may not share the same security and compliance standards), and inconsistent pricing and visibility caused by over-reliance on public platforms.
In our current period of mounting geopolitical turbulence, data sovereignty is a particular concern. While technology providers may be able to guarantee the location of certain data centre environments, the nature of modern SaaS platforms, Cloud infrastructure, and AI-powered workflows means that there is no guarantee that users' data will remain within their sovereign region, potentially leaving it vulnerable to national legislation like the US' Cloud Act, which allow governments to demand access to the data stored by Cloud providers.
This not only presents a grave risk in terms of users' privacy and security, but also means the data that powers mission-critical services like healthcare, defence, finance, and Critical National Infrastructure (CNI) may be left vulnerable to international bad actors.
Questions of data sovereignty therefore naturally lead into considerations around how we design, deploy, and scale the physical and digital foundations of emerging AI platforms that numerous organisations are exploring - the 'horsepower' that allows them to consistently deliver the desired outcomes at scale.
When infrastructure is designed with the next generation of AI workflows, and the new level of sovereignty they demand - inherent in the design, rather than retrofitted onto legacy infrastructure, the possibilities are tremendous and will drive a shift in our thinking around AI from a technology-focused approach, to an outcome-focused one.
However, while the concept is ostensibly simple, putting it into practice often proves prohibitively complex and costly, requiring the support of a trusted partner who can not only demonstrate deep knowledge of AI's ongoing evolution, but also the multiple physical and digital layers that provide the all-important horsepower, engaging with the appropriate providers to ensure their secure, seamless integration whenever necessary.
This will prove a crucial step in unleashing AI's full potential for organisations across the entire UK - from mission-critical public services that citizens depend on, to everyday interactions between businesses and their customers.
We explore this journey in greater depth in our latest report, Sovereign AI Horsepower - A British Model of Resilience, Competitiveness, and Trust. Inside, our experts consider the challenges and opportunities presented by the new generation of AI platforms and posit a new approach for bringing them to the enterprise in a way that delivers the desired outcomes with zero compromises in terms of compliance, security, or cost control. The report is free to read here for a limited time.
Frequently Asked Questions
What is sovereign AI?
Sovereign AI refers to Artificial Intelligence platforms and infrastructure designed to ensure that data, workloads and governance remain under the control of the organisation or nation that owns them. This helps maintain compliance, improve security and reduce exposure to foreign jurisdictional risks.
Why is data sovereignty important for AI?
Data sovereignty ensures sensitive information remains protected under local laws and regulations, reducing compliance risks and supporting secure AI adoption.
What are the risks of using public AI platforms?
Public AI platforms can create concerns around data residency, regulatory compliance, visibility, security and exposure to foreign legislation.
How does sovereign AI improve security?
Sovereign AI provides greater control over data location, access management, infrastructure security and governance frameworks.
What infrastructure is needed for enterprise AI?
Enterprise AI requires resilient connectivity, secure Cloud platforms, scalable compute resources, robust governance and integrated cyber security capabilities.
How does AI affect Critical National Infrastructure?
AI can improve operational efficiency and decision-making within Critical National Infrastructure, but requires strong security, compliance and sovereignty controls to protect critical services.
1233 Hits

It is no secret that cyber security is a priority for all sectors, as threats evolve in terms of frequency, scale, and sophistication. However, for Operators of Essential Services (OESs), this is just part of a larger, more complex picture. With the ongoing convergence of IT and OT and the resulting drive for an integrated approach to physical and cyber security, combined with increasingly complex compliance obligations, a more considered approach to the design and implementation of security ecosystems is needed.
A 'secure by design' approach.
It's no accident that we at Vysiion describe our delivery process, service and solution portfolio in this way - not just in relation to the cyber components of the delivery, but the systems, controls, and governance used in our delivery of mission-critical infrastructure into the most challenging environments, for the most stringently regulated sectors.
The Vysiion view, robust security is not a retrofit - it needs to be inherent in both approach and design, taking process, controls, hardware, and software into consideration, and ensuring stakeholders are aware of their roles and responsibilities.
So, taking a step back and considering how this works in practice, and from the earliest stages of a project...
An established project management methodology will include the creation of a risks and methods document, ensure the right security and risk management specialists have been engaged, and that processes are in place that follow best practice throughout each phase of delivery. A 'secure by design' approach takes this further by considering the full range of IT and OT security systems and processes that will overlay every element of the project - validated against the relevant frameworks and regulations, with the latest threat intelligence used to pinpoint the areas of greatest risk. Crucially, this includes all elements of the proposed supply chain, as these represent an increasingly common target for cyberattacks as a means of gaining backdoor access to critical data and infrastructure.
A rigorous, standards-based approach is essential, as OESs' regulatory obligations are rapidly evolving in response to the complexity of IT / OT systems, with regulations like NIS (2018) reflecting the larger attack surface created by this new breed of infrastructure.
As such, the following standards should be considered as the baseline for establishing secure, integrated IT and OT systems:
- ISO 27001. The globally recognised standard for information security.
- NIS (2018). Measures to optimise the resilience (both physical and cyber) of network and information systems.
- Cyber Assessment Framework (CAF). A systematic approach to measuring multiple aspects of cyber risk, maintained by the NCSC.
- IEC-62443. A framework for mitigating security vulnerabilities in the design and operation of critical infrastructure.
- Cyber Assurance of Physical Security Systems (CAPSS). Assurance for physical security systems.
Do not make assumptions here. The regulatory environment is increasingly rigorous, with standards and frameworks extending to organisations and market verticals previously exempt. For example, some manufacturers are now regarded as part of the UK's CNI sector and must be able to demonstrate appropriate and proportionate consideration has been given to the same regulatory and compliance goals.
Once the applicable standards have been identified, their robust principles can be adopted throughout the design and implementation phases and beyond, utilising proven methodologies like the Purdue Model to ensure dataflows and physical assets are identified and documented, and proactive monitoring of the potential attack surface is maintained (and automated, where appropriate). This should be subject to regular review using collated security data and the most up-to-date threat intelligence, and supported by a responsive maintenance capability, 24 / 7 support and monitoring, and regular auditing.
Once the applicable standards have been identified, their robust principles can be adopted throughout the design and implementation phases and beyond, utilising proven methodologies like the Purdue Model to ensure dataflows and physical assets are identified and documented, and proactive monitoring of the potential attack surface is maintained (and automated, where appropriate). This should be subject to regular review using collated security data and the most up-to-date threat intelligence, and supported by a responsive maintenance capability, 24 / 7 support and monitoring, and regular auditing.
The actual execution and impact of this approach will naturally vary from project to project and sector to sector, but it is essential that all OESs, their technology partners, and all organisations acting as part of their supply chains are ready and willing to adopt these principles, not only to fulfil their specific compliance obligations, but to ensure their services remain secure and available to citizens across the UK.
In this way, the 'secure by design' approach represents a powerful investment in your organisation's future, ensuring the continued availability and integrity of the critical product or service you provide.
Whatever the nature of your next project, if you are ready to adopt a 'secure by design' approach, don't hesitate to contact us. We will collaborate with you to establish an appropriate and proportionate approach, aligned with industry best practice and regulatory compliance, and drawing on our deep experience as an experienced supplier to the Defence, Energy, and wider CNI sectors.
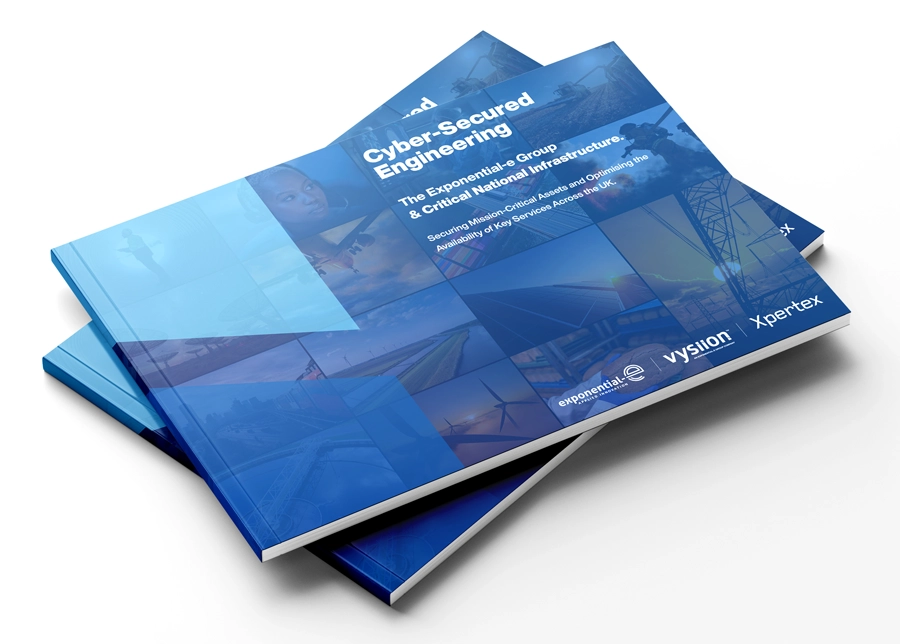
Cyber-Secured Engineering
This brochure sets out the Exponential-e Group's pedigree across the CNI sector, and our full range of capabilities, with real-life case studies of our ongoing work with leaders and innovators across the sector.
812 Hits
With manufacturing now officially incorporated into the UK's CNI sector, its overall levels of resilience and security must be reconsidered, incorporating best practice and technical innovations from other companies from across the sector (i.e. utilities and transport firms).
A key aspect of this will involve expanding manufacturers' definition of resilience beyond the safety and performance of physical machines to the integrity of the growing volumes of data generated on-site, and the cross-site connections that are increasingly powering tomorrow's interconnected workflows.
This is more than just a 'nice to have'. The recently announced Cyber Security and Resilience Bill is just the latest step in governments around the world taking proactive steps to secure public services – and the digital platforms and supply chains that support them – in an increasingly turbulent geopolitical landscape. As we close out Critical Infrastructure Security Month, the need for new standards of security and resilience across the entire CNI sector has never been higher, so let's explore the steps manufacturers can take to proactively establish this across their operations.
Optimising the resilience of manufacturing data lakes
The rise of 'smart' technologies within manufacturing operations is transforming the sector's workflows, but also significantly increasing the volumes of data that must now be stored and managed in full compliance with all CNI regulations, including the Cyber Security and Resilience Bill, EU NIS 2, and eCAF. Storing these large volumes of structured and unstructured data onsite will likely prove impractical, introducing a serious financial and operational burden, but at the same time, the need for real-time visibility of manufacturing operations, along with increasingly complex security and compliance challenges, means a full-scale move to the Cloud will not necessarily be viable.
Colocation offers an alternative way forward here, offering manufacturers a single answer to a range of data hosting challenges. By relocating specific volumes of data to dedicated space in external, geographically dispersed data centres, while keeping others on-site – potentially as part of a wider hybrid Cloud strategy – manufacturers will enjoy a whole new level of flexibility in terms of how they store and manage their data that will, in turn, bring them up to the standards of operational resilience that CNI demands.
Of course, putting all this into practice requires a world-class hosting environment…Enter your text here...
How Vysiion are providing the foundation for more resilient manufacturing across the UK
This is why Vysiion continues to maintain our presence in the Tier III Ark data centres – the Government's hosting environment of choice and the only data centres with pan-government accreditation at all security levels. As an active presence in these highly secure, eco-friendly hosting environments, we have helped organisations across a range of sectors develop approaches to data hosting that support the most complex workflows and compliance obligations, offering hands-on support throughout the migration process to minimise any disruption. This includes connections to the secure private networks utilised across manufacturing operations, where necessary.
Our presence in the Ark data centres, combined with our deep experience around 'smart' technologies, the ongoing convergence of IT and OT, and the manufacturing sector's unique workflows and operational models – plus comprehensive cyber security capabilities – means we are able to help you manage your data in the way that best suits your operations, your budget, and your evolving compliance obligations.
Just contact us if you would like to discuss your own manufacturing operations' data hosting requirements in greater depth.
Cyber-Secured Engineering
This brochure sets out the Exponential-e Group's pedigree across the CNI sector, and our full range of capabilities, with real-life case studies of our ongoing work with leaders and innovators across the sector.
545 Hits
The Cloud has fundamentally changed the way organisations across a range of sectors design, manage, and scale their IT infrastructure. In many cases, this has allowed them to stay abreast of unexpected shifts in the digital landscape while retaining full control of ongoing costs and turning their growing volumes of data into a powerful source of business insights. But when it comes to digital transformation, there's no such thing as a one-size-fits-all solution. At Vysiion, we've seen this over and over again throughout our work with organisations operating in some of the harshest environments, with some of the most rigorous security and compliance requirements.
In many such cases, where critical applications and data need to be available in as close to real-time as possible, the only answer is to locate hardware at the edge, which naturally limits opportunities for Cloud transformation. However, now more than ever, technology tends to evolve to fulfil the most specific requirements, especially when organisations and their technology partners work in close collaboration to drive new innovations. In fact, we may already be seeing such solutions emerging in response to these singular requirements…
Hyperconverged Infrastructure opens the door
to next-gen hybrid Cloud
Azure Stack HCI, for example, offers a new approach to Cloud transformation that enables specific systems to be maintained at the edge, where necessary – a true hybrid approach that allows Cloud platforms to be seamlessly integrated with edge computing environments to achieve the desired functionality.
The use of containerisation and virtual machines offers a level of control and flexibility that would be difficult, if not impossible, to execute exclusively with on-premises systems, while still ensuring data sovereignty and compliance obligations can be met. For additional layers of security and resilience, integration with Azure Security Center and Azure Defender is available, along with built-in redundancy.
All of this can be manged through a centralised control panel, allowing for complete visibility of operations and data flows, even for the most remote locations.
This approach has huge implications for AI and IoT projects at the edge, allowing for real-time monitoring and analytics, combined with intelligent automation of routine processes to maximise operational efficiency.
But, once again, this is not without its limitations, as standard hardware is rarely suitable for the harshest, most challenging environments – such as military zones, highly remote energy sites (e.g. oil rigs and offshore windfarms), or industrial conditions – which may make Azure Stack HCI challenging to implement.
Is ruggedised Azure HCI the ultimate edge computing solution for Defence, CNI, and Manufacturing?
It is clear that Azure Stack HCI's potential across these sectors is enormous. We must therefore consider how it can be implemented in such a way as to access all the possible benefits, while still maintaining the security and resilience of critical infrastructure in situations when environmental conditions may lead to failures.
However, based on a range of ongoing conversations with our customers and technology partners, we would argue that such measures are already available. By combining Azure HCI's full range of capabilities with high-quality, ruggedised hardware, true 'always-on' operations can be established, with seamless, highly secure flows of critical data between edge devices and the Cloud.
Whatever environments you operate in, and whatever your digital goals are at the edge, in the Cloud, or both, do not hesitate to contact us. Drawing on our deep experience designing bespoke digital transformation solutions to the most rigorous specifications, our teams will work closely with you to achieve your long-term goals, and so help establish a new standard of digital best practice across the most challenging sectors.
Cyber-Secured Engineering
This brochure sets out the Exponential-e Group's pedigree across the CNI sector, and our full range of capabilities, with real-life case studies of our ongoing work with leaders and innovators across the sector.
674 Hits
Like a great many of you, as soon as we had some sunny weather recently, I was all set to break out the barbecue. But my plans were soon scuppered when I realised I needed a new can of Calor gas. Undeterred, I checked for local stockists on Calor's website and got on the phone to check who had some available. On each occasion, no-one answered the phone.
So, after multiple failed attempts, I just got in the car and drove to every petrol station in the area until I found someone with Calor in stock. So, our barbecue did happen in the end, but my little adventure actually demonstrates a wider challenge that the retail and hospitality sectors (and others) are facing at the moment.
With retail and hospitality environments, most things have moved online (e.g. bookings, opening hours, or to check stock if click-and-collect is available), but there are still lots of scenarios where people still call up. For example:
"Sorry, I'm running 10 minutes late, but I want to keep my reservation."
"Are you dog friendly?"
"Are you open this bank holiday?"
The challenge here is that many businesses in retail and hospitality (pubs and restaurants, for example) are unlikely to be running dedicated call centres, and their staff are going to be on their feet all day, attending to guests rather waiting by the phone. If a customer can't find the information they're looking for online and isn't able to speak to a member of staff, then their options are to risk it and make a booking or order regardless, continue to wait on hold, or simply take their business elsewhere. None of these options make for a great customer experience.
So, how do we strike the right balance between operational efficiency and that all-important human touch? While it may seem contradictory at first glance, agentic AI potentially holds the answer.
AI agents have improved to the point where their voices are convincing enough to serve as the first point of contact over the phone, just as is now the case on many websites. This way, a caller is greeted straight away by a friendly voice rather than an automated menu or the dreaded on-hold music - an immediate improvement in the overall customer journey. But this is the clever part... Voice recognition and sentiment analysis enable AI agents to make the decision as to whether a call would be best handled by a human agent and, if so, direct the caller to the right person.
So, let's say a restaurant gets a call from someone who wants to make a reservation... The AI agent can automatically check which tables are available, set out the options, and make the booking without a human member of staff needing to get involved. On the other end of the spectrum, if a customer calls with a question that requires a specialist's input or wants to book a party for 100-plus people, these will be directed straight to the appropriate member of staff.
So, when it's applied strategically, with the ideal customer journey in mind, agentic AI offers rich opportunities to optimise customer
contact over the phone in the same way as many organisations are already doing across other channels, not only in terms of making sure someone is there to answer the phone, but also making sure their desired result is achieved as seamlessly as possible.
When AI agents manage customer interactions in the way describe above, they're not only capable of intelligently routing the conversation, but also transcribing it, pruning anything irrelevant (small talk, for example), and uploading the whole thing to the CRM system - something that would not be practical to do manually, even for dedicated contact centre teams. This can be combined with interactions across other channels to build deep customer profiles that can support personalised marketing, as well as practical things like automated reminders about reservations, or when a requested item has come back in stock.
This also opens up new ways to measure agent performance and wellbeing, ensuring everyone is delivering the expected quality of service, and customer satisfaction targets are consistently met. By analysing the data gathered throughout customer interactions across all channels, trends can be identified, successes built upon, and measures put in place to remedy any recurring problems, such as providing additional training or support where necessary.
There's understandably a lot of hype around AI platforms right now, but customer contact is one of the areas where it is most definitely proving truly transformative, ensuring that customers are always able to make contact through whichever channel they prefer, and enjoy seamless, stress-free resolutions. When we step back and take an objective look at the different points of contact with customers, we will get a clearer understanding of where agentic AI can add the greatest value, adapting to the technology to suit our customer service goals rather than the other way around.
Finally, some food for thought... Someone recently created an AI chatbot to call every pub in Ireland and enquire about the cost of a pint of Guiness, using this data to generate a price map of the whole country. How many of those interactions already involved bots talking to bots, and how likely is this to become a standard part of business' customer interactions? Interesting times for the entire sector for sure.
If you're interested in exploring potential opportunities to implement agentic AI, or any other aspect of your customer contact systems and processes, just get in touch (even by phone, if you prefer!).
Exponential-e & Retail
Our Retail brochure offers a comprehensive overview of how we draw on a deep understanding of the sector's singular challenges, an evolving technology ecosystem, and a highly consultative approach to offer bespoke solutions that help staff deliver their best for every customer - both online and in person.
1268 Hits
The ongoing evolution of our nation's Critical National Infrastructure (CNI) requires large-scale CAPEX investment in core infrastructure, along with the introduction of digital initiatives that support the convergence of physical and digital systems, enhancing performance, efficiency, and availability. This presents a multi-dimensional challenge for CNI organisations, who are often forced to accelerate or adapt their long-term transformation roadmaps, whether this means scaling, restructuring, preparing for an exit or investment, or a combination of all three.
In parallel, the increasing deployment of digital technology amongst Operators of Essential Services (OESs) has led to a range of new security and compliance challenges. When shareholders are made aware of these risks, they - correctly, demand reassurance that their high-value investments will be protected.
For this reason, technology partners supporting CNI verticals must be alert to the requirements of a diverse stakeholder community, offering informed advice throughout the investment process, providing an accurate assessment of risk and compliance challenges, and translating often conflicting priorities into deliverable actions that will drive business growth.
Let's consider how this should work in practice...
Enabling data-driven decision-making throughout mergers and acquisitions
When physical and digital assets are seamlessly and securely interconnected, operators enjoy access to rich veins of real-time data around the status of key platforms. This data can be used to accurately benchmark all security and operational risks against technical and regulatory compliance, establishing their potential impact on service availability and, in turn - the predicted ROI.
When this level of visibility has been achieved, improvements in both efficiency and profitability are unlocked, benefiting the wider stakeholder community and enabling more informed decision-making throughout every stage of mergers and acquisitions, including:
- Pre-acquisition due diligence: Identifying technical debt and flaws, establishing security and compliance risks with a concrete value for their remediation.
- Post-acquisition investment: Establishing OPEX costs needed to support effective systems and processes to ensure the continued security and compliance of critical infrastructure.
- Exit readiness: Creating a definitive, auditable log of critical assets, reflecting full regulatory compliance and the ability to meet investor scrutiny.
Specialist IT / OT advisory and support to protect investments
This role can be taken further, with technology partners serving as advisors to PE firms and mid-cap boards, providing them with the technical and operational oversight they need to protect and validate their investments. This should begin with rigorous technical (i.e. the IEC62443 standard) and regulatory (i.e. NIS-2018 / CAF) assessments, conducted in line with the overall risk appetite and corporate strategy. Once these information streams have been established, they can be used to augment CIO and CISOs' capabilities, bridging the knowledge gap between enterprise IT and OT systems and optimising governance and risk management.
When it comes to making informed investments in critical infrastructure, the value of objective, strategic guidance from experienced specialists cannot be overstated. Technology partners who are able to support IT leadership in this way will evolve from pure providers to true enablers of business growth, providing tangible value to investors while optimising the performance, security, and availability of critical services.
If you require guidance around any planned or existing investments in CNI infrastructure, contact us to arrange a consultation of potential risks and a detailed assessment of how they can be mitigated, based on globally recognised standards and our deep experience across multiple CNI verticals, including Energy, Utilities, Transport, Defence, and Industry.
Cyber-Secured Engineering
This brochure sets out the Exponential-e Group's pedigree across the CNI sector, and our full range of capabilities, with real-life case studies of our ongoing work with leaders and innovators across the sector.
936 Hits
Across the Hospitality & Leisure sector, more and more data is generated and stored than ever before, throughout every stage of the guest experience. From the initial check-in, to accessing amenities, and post-visit engagement, the modern guest experience is truly interconnected, offering hospitality professionals numerous opportunities to build brand loyalty and develop powerful USPs. It's a transformative time for the sector as a whole, but these growing volumes of data present an extremely attractive target for bad actors. We just have to look at the growing number of high-profile breaches in recent years - where the targets have been left unable to trade and forced to contend with operational disruption, financial penalties, and reputational damage – to see the potentially irreparable effects of such attacks.
It's no surprise that guests expect concrete reassurance that their data will remain secure throughout the duration of their stay and beyond. As a result, organisations across the sector are investing in their cyber security ecosystems, phasing out legacy systems in favour of Security Information and Event Management (SIEM) and Security Orchestration, Automation, and Response (SOAR) platforms that provide fully centralised control and visibility of highly dispersed sites.
The challenge here is that the right digital investments are just the first step towards developing a robust cyber security posture. As seasoned hospitality professionals will already be very much aware, when people and technology come together, great things happen. And it's the same with cyber security.
SIEM and SOAR platforms provide rich veins of actionable, real-time security data in the form of logs, alerts, and analytics. However, far too many organisations investing in such platforms fail to consider how this data will be acted upon, and how a real security alert will be managed. Indeed, in many cases, their internal IT teams simply lack the time and resources to do so - a situation compounded by the growing diversity of cyber security portfolios, where multiple platforms from different providers have been integrated.
This is where a Security Operations Centre (SOC) becomes essential. A world-class SOC combines skilled analysts, defined processes, and supporting technologies to monitor, investigate, and respond to potential threats in real time. Without this operational layer, the expected ROI of digital platforms all-too-often fails to materialise, and in a worst-case scenario, the lack of defined processes may even lead to a security breach going undetected.
However, for many hospitality providers, building and maintaining an effective SOC in-house can be prohibitively challenging, and so there is a strong case to be made for implementing managed SOC services, as many across the sector have already found. Here, trusted partners' own specialists provide round-the-clock monitoring and response, acting as an extension of internal teams. This approach allows organisations to develop a stronger, more agile security posture, while simultaneously enabling internal resources to remain focused on delivering exceptional guest experiences.
So, if you're in any doubt about your overall security posture - whether that's systems, processes, or both - don't hesitate to contact us. Based on a thorough evaluation of your existing systems and processes, we will work closely with you to design, deploy, and maintain a cyber ecosystem that fully supports your day-to-day operations, freeing you to focus on delivering seamless, exceptional experiences for every guest, every time.
A comprehensive overview of digital transformation for the entire Hospitality & Leisure sector.
- Building your guest experience on the right digital foundation.
- Ensuring your infrastructure continues to evolve with your business.
- Turning one-off guests into loyal, repeat customers.
1320 Hits
An AI-powered Approach to Delivering Local Government Services
The UK's local councils are challenged on a growing range of fronts. Budgets and resources are shrinking, but citizens' expectations around the quality and availability of the full range critical services must still be fulfilled, whether this involves making sure the bins are always collected on time, or ensuring the most vulnerable are able to access the support they need. Indeed, at the time of writing, one local council's list of services runs to seventeen pages, with over four-hundred individuals involved in their delivery.
Put simply, councils' frontline staff are being forced to do more with less, making these highly complex service environments prime candidates for intelligent automation. But, as is often the case when it comes to the deployment of agentic AI technologies - there's a lot to consider if the initial investment is to deliver the desired outcomes. Consider the following:
- 66% of councils have trouble understanding where AI can deliver the greatest value.1
- 43% of local councils saying the lack of clear use cases is a barrier to AI adoption.2
While many councils have already realised agentic AI's applications for purely transactional services (e.g. the payment of parking fines or council tax), it is clear that a deeper understanding of its potential applications is still needed.
One common misunderstanding around AI is that it is best used to replace human agents wherever possible, but this is a fatal misconception. This technology's full potential is as an enabler and enhancer of human expertise and experience, allowing frontline staff to consistently deliver their best while simultaneously ensuring their wellbeing is protected.
Consider a list of services like the one we touched on at the beginning of this article - a quite typical service wrap for local Government organisations. No human agent could sensibly be expected to be able to deliver that many services, but at the same time, hiring individual specialists for every area is not going to be practical when doing more with less is the order of the day.
Agentic AI offers a third way, automatically putting the information and resources agents need to deliver successful resolutions right at their fingertips, without requiring them to manually parse complex knowledge libraries.
AI's ability to translate high volumes of data into an actionable form in real-time is unprecedented. Critically, this does not just have to mean formal knowledge bases that Government departments maintain themselves - it can also browse relevant websites, PDFs, and other sources of information, collating their findings in agents' dashboards in response to the most specific queries, including providing practical steps towards a resolution. This not only significantly eases the pressure on frontline staff, but can also reduce the time and expense involved in training new agents or broadening the capabilities of existing ones.
AI's ability to translate high volumes of data into an actionable form in real-time is unprecedented. Critically, this does not just have to mean formal knowledge bases that Government departments maintain themselves - it can also browse relevant websites, PDFs, and other sources of information, collating their findings in agents' dashboards in response to the most specific queries, including providing practical steps towards a resolution. This not only significantly eases the pressure on frontline staff, but can also reduce the time and expense involved in training new agents or broadening the capabilities of existing ones.
At Exponential-e, we're already working closely with a number of Government organisations (and numerous others from across the public and enterprise sectors) to bring these concepts to life and establish a clear standard of best practice around where and how agentic AI is implemented. These "cyber advisors", as they are increasingly called, are transforming the way local Government's contact centre environments operate, ensuring citizens enjoy the fastest possible resolutions, while simultaneously freeing up time and resources that can be reinvested in other public services.
Of course, this must all begin with the right foundation - specifically, a thorough assessment of an organisation's current customer journey, which will reveal where the implementation of agentic AI will bring the greatest possible benefits, and how the necessary changes can best be executed. Contact us today to arrange your own consultation and take the first step towards building your own team of world-class cyber advisors.
A secure digital foundation for better citizen outcomes, operational resilience, and long-term value.
Public sector organisations are under pressure to deliver more with less while meeting rising expectations for secure, always-available services. This guide shows how an integrated approach to connectivity, cloud, cyber security, and communications creates the resilience, scalability, and compliance government demands – turning digital strategy into real community impact.
1554 Hits
An exceptional customer journey extends far beyond the initial point of sale. And nowhere is this truer than for subscription-based businesses, whose continued success is based on delivering consistently seamless, high-quality experiences throughout each customer's time as a subscriber - from the initial sign-up through to the point where they decide to terminate their subscription for whatever reason.
Indeed, these new models have transformed the way many businesses interact with their customers, applying lessons learned from established subscription-based services, such as gyms and streaming services. From both traditional retailers and ecommerce specialists offering scheduled deliveries of household essentials, groceries, and entertainment products, to the now-ubiquitous software-as-a-service model and premium subscriber options on popular social media platforms, there are numerous channels for forward-thinking businesses to establish 'sticky' streams of income, with more still to reveal themselves.
However, the rules around offering and managing subscriptions and memberships of any sort are about to change, particularly with regards to cancellations…
Throughout 2026, the Competition and Markets Authority (CMA)'s regulations around buyer protection and autorenewals are going to evolve, as part of the existing Digital Markets, Competition and Consumers Act 2024 (DMCC Act), in order to help consumers avoid getting trapped in unwanted subscriptions. Organisations found to be in violation of these new regulations can expect to face fines of as much as 10% of their annual revenue.
As a result, any retailer that offers subscriptions or memberships of any kind must be aware of how these changes will impact them in the months ahead and, adapt their systems and processes to ensure they remain fully compliant with all applicable regulations, and - most importantly - ensure that they are still able to offer a world-class experience for their subscribers.
So, what's about to change and how can we best prepare?
- Specific pre-contract information must be provided. The DMCC Act distinguishes between key pre-contract information and full pre-contract information. Both must be provided in full at the initiation of the contract, or the customer will not be bound by the stated terms. Compulsory elements include:
- Full details of payments, include frequency and amounts.
- Minimum total liability.
- Schedule of reminder notices.
- Full cancellation rights.
- Reminder notices will be compulsory. It is no longer enough to assume a customer will automatically want to renew their subscription. Reminder notices must be sent in advance of the renewal date.
- Cooling-off periods will also be compulsory. This applies to both new subscriptions and renewals. Customers must have 14-day window to cancel their subscriptions without penalty.
- Cancellations must be as simple as possible. Cancellation instructions must be provided, and the process must not include any unnecessary steps. This also applies to online subscriptions. Confirmation must be provided within 24 hours.
There's certainly a lot to consider here, but rather than treating these changes as onerous compliance obligations, why don't we treat them as an opportunity to reconsider the overall subscriber journey, and look for new opportunities to enhance it?
Traditionally, when a customer wishes to cancel a subscription or membership, they've done so by speaking to an agent, who will then have the opportunity to discuss their reasons for cancelling and potentially offer some perks to change their mind. In light of the changes mandated by the new DMCC, this is unlikely to be practical in the majority of cases, when customers are able to unsubscribe with a single click. This has the potential to create a serious loss leader for subscription-based businesses whose customer engagement strategy is based on an initial discount or free gift (e.g. the first month's delivery is free, after which the subscriber pays the usual rate), as there is nothing to stop customers hitting 'unsubscribe' right before their first payment is due.
However, with agentic AI and intelligent automation currently transforming both the contact centre environment and the wider customer journey, numerous opportunities have presented themselves to ensure full compliance can seamlessly co-exist with personalised experiences that maximise long-term retention and build brand loyalty.
For example, if someone is looking to cancel via a page on your website and you have already implemented a chatbot function that they use to request a cancellation, the bot can automatically engage a real customer service agent, who can discuss the reasons for their cancellation, provide any hands-on support they need, and (ideally!) offer any perks or resolutions that will entice them to stay.
If your contact centre environment and chatbot functions have been intelligently integrated (as they should be!), these interactions can then be utilised to drive further optimisations, such as ensuring cancellation requests are routed to agents who have the best records of retaining customers, or ensuring agents don't invest their time and effort on accounts that have no realistic chance to renewing their subscriptions. For example, AI-based analytics can identify trends in customer data, such as individual addresses that have signed up for multiple trials but never made a purchase, which will allow agents to focus their attention where it will prove most effective.
And of course, the best approach to minimising cancellations is ensuring customers never want to cancel to begin with! All the data gather through customer interactions - whether it's with an agent or chatbot - can help build up more accurate, comprehensive customer personas that support highly personalised offers, helping to maximise the number of subscription renewals.
Above all, while regulations evolve and customer expectations naturally shift, the value of a personalised experience, delivered by an attentive, knowledgeable professional is a constant for the Retail sector. If we keep this in mind while making full use of the possibilities AI-powered automation offers us, the opportunities will be tremendous.
If you'd like to take a deep dive into your own customer journey and identify where the intelligent application of new technologies could make that all-important difference, just get in touch.
Exponential-e & Retail
Our Retail brochure offers a comprehensive overview of how we draw on a deep understanding of the sector's singular challenges, an evolving technology ecosystem, and a highly consultative approach to offer bespoke solutions that help staff deliver their best for every customer - both online and in person.
1698 Hits
The Challenge
The Customer was working through a partnership disaggregation from a consortium IT Service to regain IT autonomy, underpinned by a strategic MSP partnership to augment limited in-house IT skills. The Customer went to market to seek a single supplier to accelerate the immediate requirement and support their long-term digital strategy to modernise IT with 'better use of data for insights and improvements'. With data sovereignty being a key concern for the Customer, a UK-based service provider was essential.
The Solution
The Customer engaged Exponential-e to deliver a fully managed IT service, including:
- End to end migration of critical systems and workloads into Azure.
- UK-based Managed Cloud Services for Azure-based workloads.
- Dedicated IaaS for localised/sensitive workloads
- UK-based user service desk for ~400 end users.
- Onsite support function.
- Lifecycle management of end user devices.
- Local Area Network deployment and management.
- Wide Area Network.
The full stack solution provided excellent value to the Customer, allowing them to accelerate the disaggregation through a single supplier partnership.
The solution was fully delivered by Exponential-e delivery services - Project Management, Azure Migration Specialists, User Specialists, Service Management and Onboarding Teams over a period of eight months. This ensured the project was delivered on time and budget to meet the transition targets defined by the Customer.
Solution Benefits
- Deployment and configuration of CAF-aligned Azure Landing Zones.
- Azure Migrate-based migration of Windows Server and Linux Virtual Servers to Azure.
- Migration of 9TB file data to Azure Files.
- Infrastructure resiliency with Azure Site Recovery and Azure Backup.
- Deployment of Intune and MEM for unified device management.
- Unified identity services through Microsoft Entra.
- Cloud Backup for Microsoft 365.
- Seamless cutover of user support services.
- Optimised wireless network coverage within key user locations.
- Three-Year Azure Savings Plan for cost control over contract terms.
Azure Stack HCI
The Good, The Bad & The Hybrid
In this exclusive whitepaper from Exponential-e's Cloud transformation specialist, James Pearce, discover how the next generation of hyperconverged infrastructure is transforming the way organisations design, deploy, and manage cutting-edge IT infrastructure, along with a proven roadmap for its successful implementation.
1407 Hits
▲
Register your interest now
Register your interest now
Register your interest now
Reserve Your Spot Today
AI Strategy, Roadmap & Operating Model
From Ambition to Enterprise Execution
AI Platforms, Data & Architecture
Building the Foundation for Scalable AI
AI Use Cases, Agentic AI & Business Transformation
Turning AI into Real Operational Impact
Trusted AI, Security & Governance
Scaling AI with Confidence and Control
Register your interest now
AI Use Cases, Student Experience & Business Transformation
Turning Complexity into Real Operational Impact
AI Strategy, Roadmap & Operating Model
From Ambition to Enterprise Execution
Applications and Supply Chain - How to Secure
End-to-End Visibility and Assurance Across NHS Digital Ecosystems
Next Steps After DSPT
From Point-in-Time Compliance to Continuous Cyber Resilience
What Does Partnership Look Like
Collaborative Assurance, Shared Responsibility, and Secure Innovati
Event capacity full
Register for waiting list